
In this article
To communicate securely with other servers (vCenter Server, databases, LDAP, Single Sign-On and others), Orchestrator must be able to verify their identity. For that, you may need to import the remote server’s SSL certificate into the Orchestrator trust store. Without it, workflows that talk to that server fail with a certificate error like this one:

Tested on: VCF Operations Orchestrator 9.1.1 (checked Nov 2026: the Library workflow is still available) and vRealize Orchestrator 8.x (original steps, 2022).
Two ways to trust a certificate
You can import a certificate into the trust store either by connecting to a specific URL, or directly from a PEM-encoded file.
| Option | Description |
| Import from URL or proxy URL | The URL of the remote server: https://your_server_IP_address or your_server_IP_address:port |
| Import from file | Path to the PEM-encoded certificate file. |
In this post, we’ll focus on importing a certificate from a PEM-encoded file. For URL-based import, simply use the Library workflows.
Step 1: Generate the PEM file
Prerequisites
Find the fully qualified domain name of the server you want Orchestrator to connect to over SSL.
Procedure
- Log in to the Orchestrator appliance over SSH as root.
- Run this command to retrieve the remote server’s certificate:
openssl s_client -connect host_or_dns_name:secure_port
- If you use a non-encrypted port, add
-starttlsand the required protocol:
openssl s_client -connect host_or_dns_name:port -starttls smtp
- Copy the text from the
-----BEGIN CERTIFICATE-----tag to the-----END CERTIFICATE-----tag into a text editor, and save it as a file on your local system.
Step 2: Import the PEM file
You can import the file using a Library workflow or, on older versions, Control Center.
Option A: Library workflow (all versions)
- Log in to the Orchestrator client.
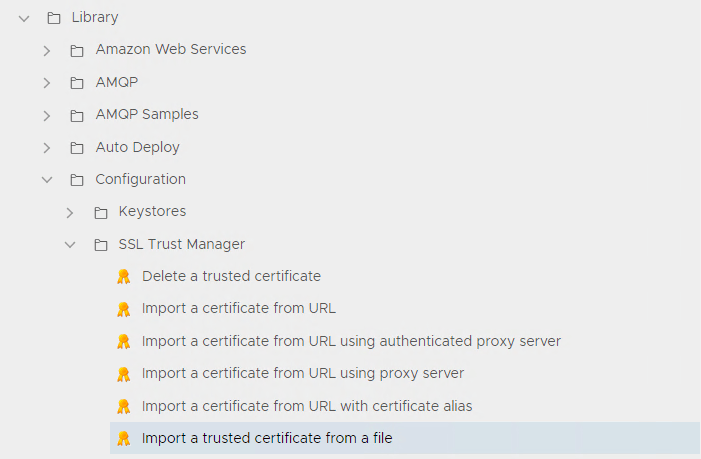
- Go to Workflows under Library > Configuration > SSL Trust Manager.
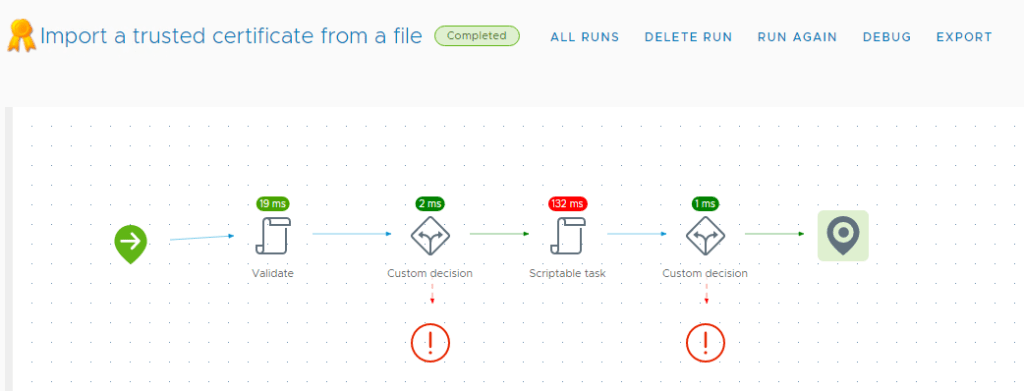
- Run the workflow Import a trusted certificate from a file.
- Browse to the certificate file and click Run.

- The workflow should complete successfully.
Option B: Control Center (8.18 and earlier)
- Log in to Control Center as root.
- Go to the Certificates page.

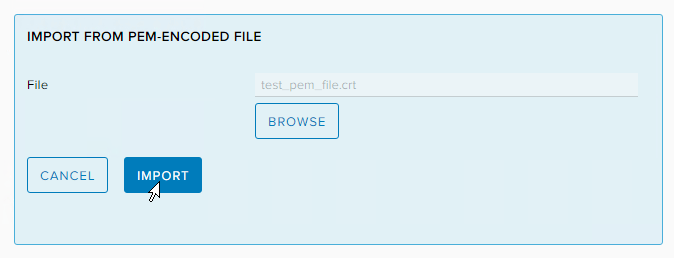
- On the Trusted Certificates tab, click Import and select the Import from a PEM-encoded file option.

- Browse to the certificate file and click Import.
Result
You’ve imported the remote server’s certificate into the Orchestrator trust store. Run the workflow that talks to that server again, and the certificate error is gone.
Things to watch out for
- No Control Center from 8.18.1 onwards. Control Center was removed starting with Orchestrator 8.18.1, and VCF Operations Orchestrator 9.x doesn’t have it either, so use the Library workflow (Option A) there.
- Certificates get renewed. When the remote server’s certificate changes, import the new one, or the same error comes back.
Wrapping up
Two steps: grab the certificate as a PEM file, then import it with the Library workflow. If you run into a different certificate error, feel free to share it in the comments. See you in the next post.
Discover more from Cloud Blogger
Subscribe to get the latest posts sent to your email.
Enjoyed this post?
Was this helpful?






Leave a Reply